Our product
Optimux
Security audits, CVE scanning and monitoring for Linux servers, in one platform. We built it and run it ourselves.
Visit optimux.io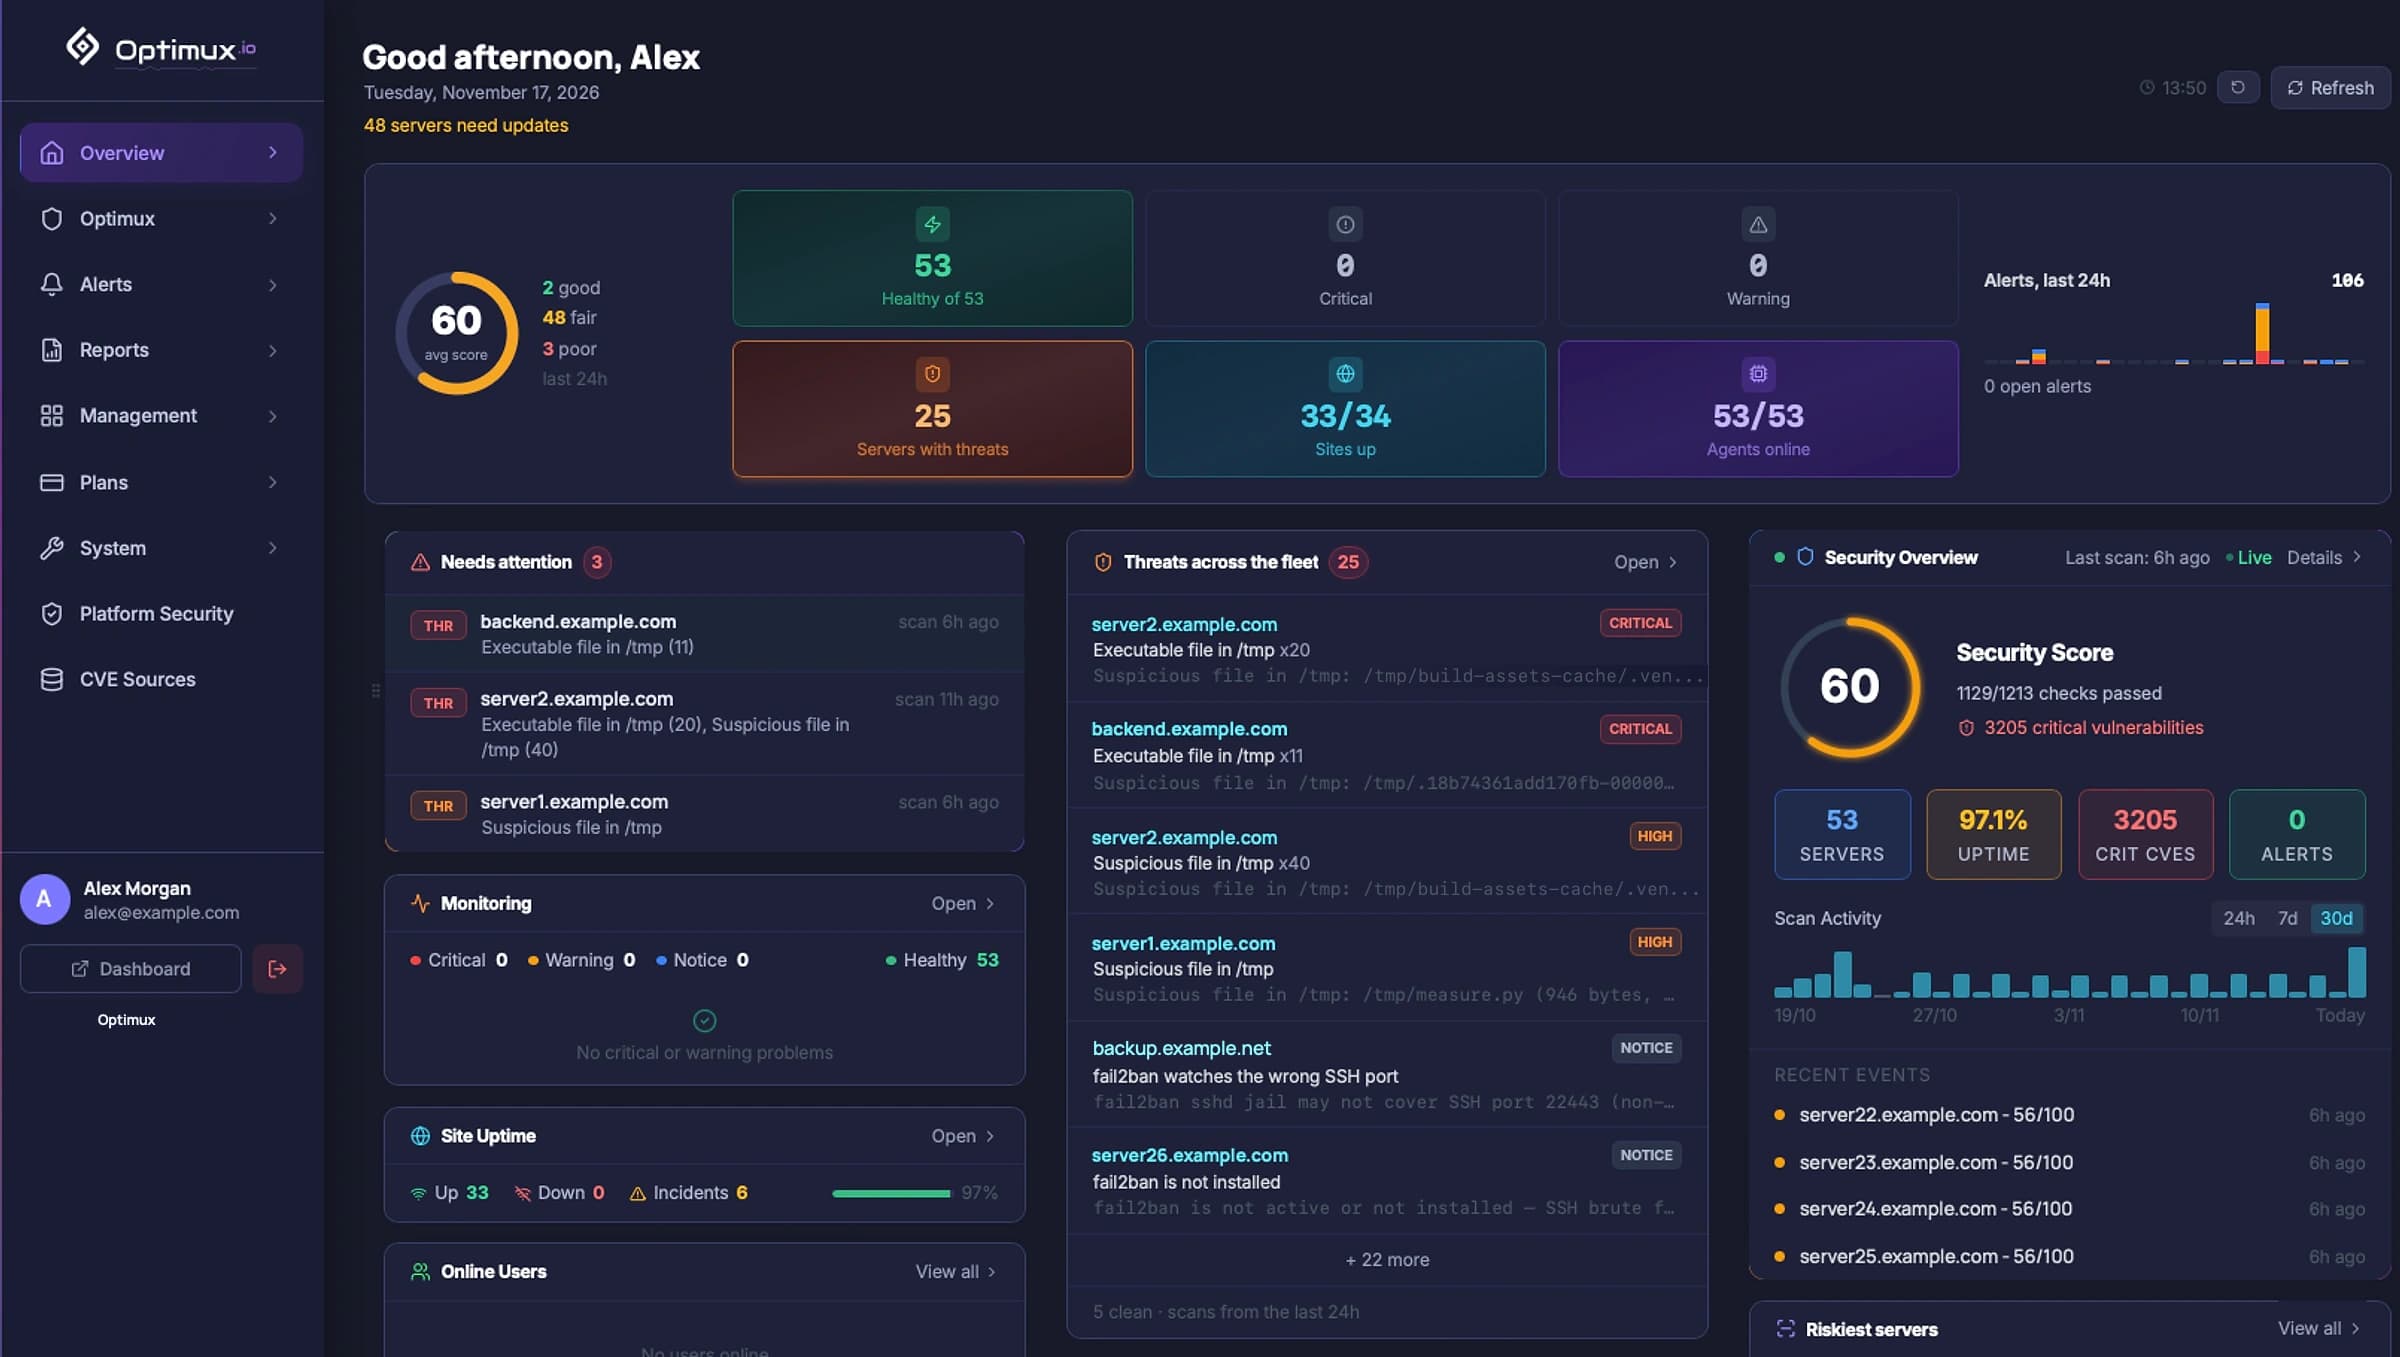
What it checks
Security audit
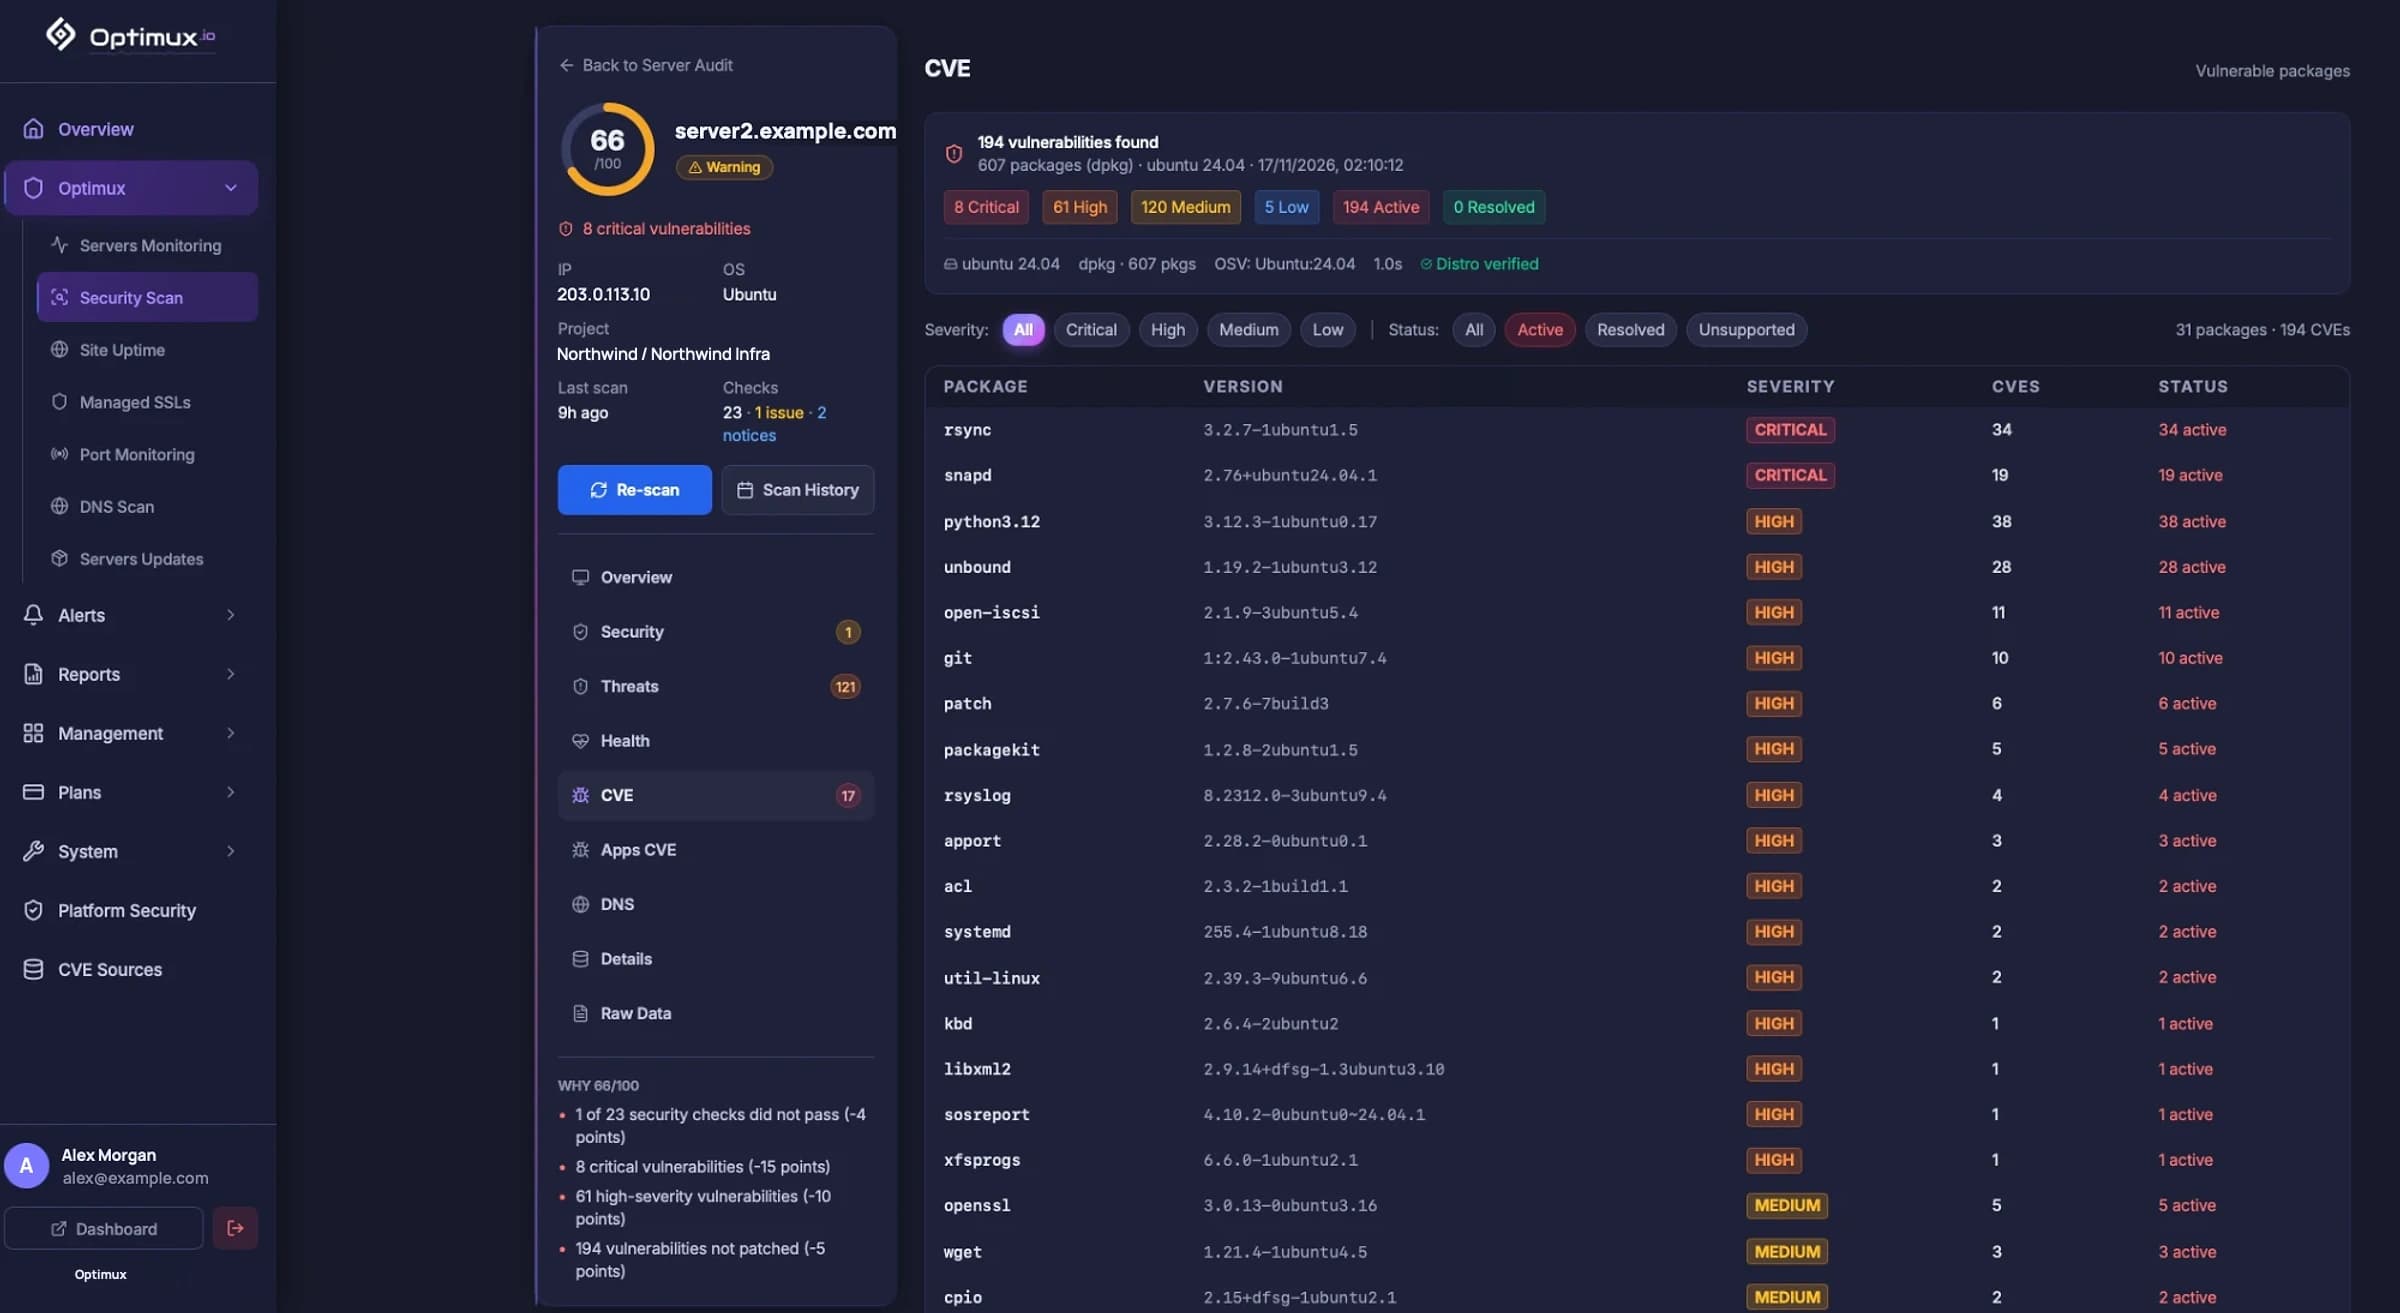
SSH, users, file permissions, services and pending updates checked on every server, with a score and the reasons behind it.
CVE scanning
Installed packages checked against each distribution's own CVE tracker, plus npm, Composer and PyPI lock files, WordPress and PHP builds.
Threat detection
Reverse shells, crypto miners, odd outbound connections, persistence in crontab and database ports open to the internet.
Server monitoring
CPU, memory, disk, load and network live, with thresholds per server and hardware health on physical machines.
Uptime and SSL
HTTP, TCP, ping and keyword checks, SSL grades, and certificate and domain expiry.
DNS and ports
SPF, DKIM, DMARC, record changes and blacklists, and port checks from outside.
Alerts go to email and Slack and repeat until someone acknowledges them. Reports come as PDF, on demand or every month.
How it reaches your servers
Optimux talks to a small agent on each server over TLS 1.3, from one fixed address, and the dashboard shows the firewall rule for it when you add a server. The agent runs as its own user, not root, answers only to its server's token and runs a fixed list of commands. Scans are read-only.
Two-factor sign-in is available, and each customer's data is kept apart from every other's. The platform is hosted in Germany and carries no third-party trackers.
- Runs on
- Ubuntu, Debian, RHEL, CentOS, AlmaLinux, Rocky Linux, CloudLinux, Oracle Linux, Amazon Linux and Fedora, on x86_64 and ARM64.
- OS package CVEs checked on
- Ubuntu, Debian, RHEL, CentOS, AlmaLinux, Rocky Linux and CloudLinux.
Built by engineers who run servers
Optimux is made by Private DevOps, and we run it in production ourselves. When it finds something you would rather not fix alone, our engineers can do it for you.